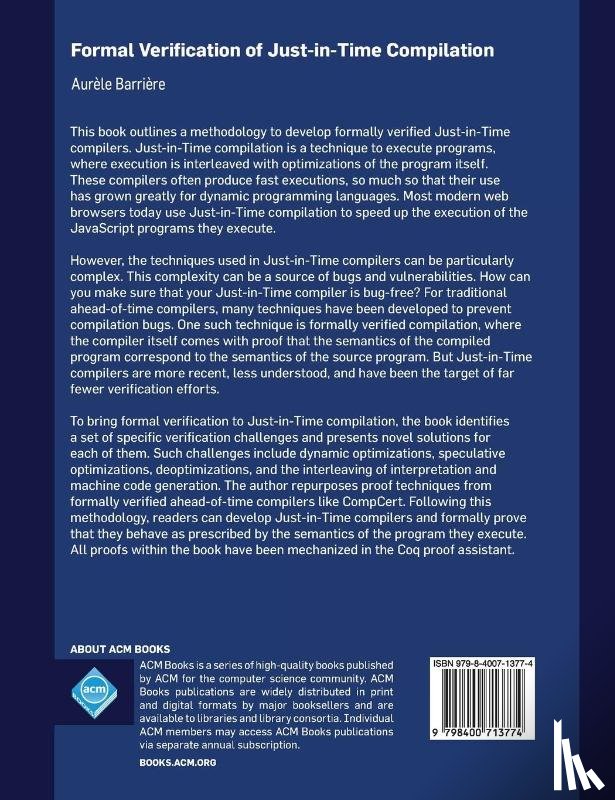
Explore a methodology to design formally verified Just-in-Time compilers that merge rapid program execution with strict correctness. Navigate challenges from dynamic, speculative, and deoptimized optimizations interleaved with code generation, with each phase validated by Coq proofs for compiler rigor.
I have a question about the book:
'Formal Verification of Just-in-Time Compilation - Barriere, Aurele'.
Fill in the form below.
We will respond as fast as possible.
We value your privacy
We use cookies to measure traffic, improve Boekstra and let Google tailor ads to your interests. You can keep using the site either way — even if you decline. More info